


When a tracking domain stops working for people on one mobile carrier or one home internet provider, there is usually no error anywhere in Everflow. Clicks simply stop arriving from that provider while everything else looks normal. ISP Trends is the report that makes that pattern visible.
This article covers what the report shows, how to read a drop, and what to do when a provider does appear to be blocking one of your domains.
Where To Find ISP Trends
Open
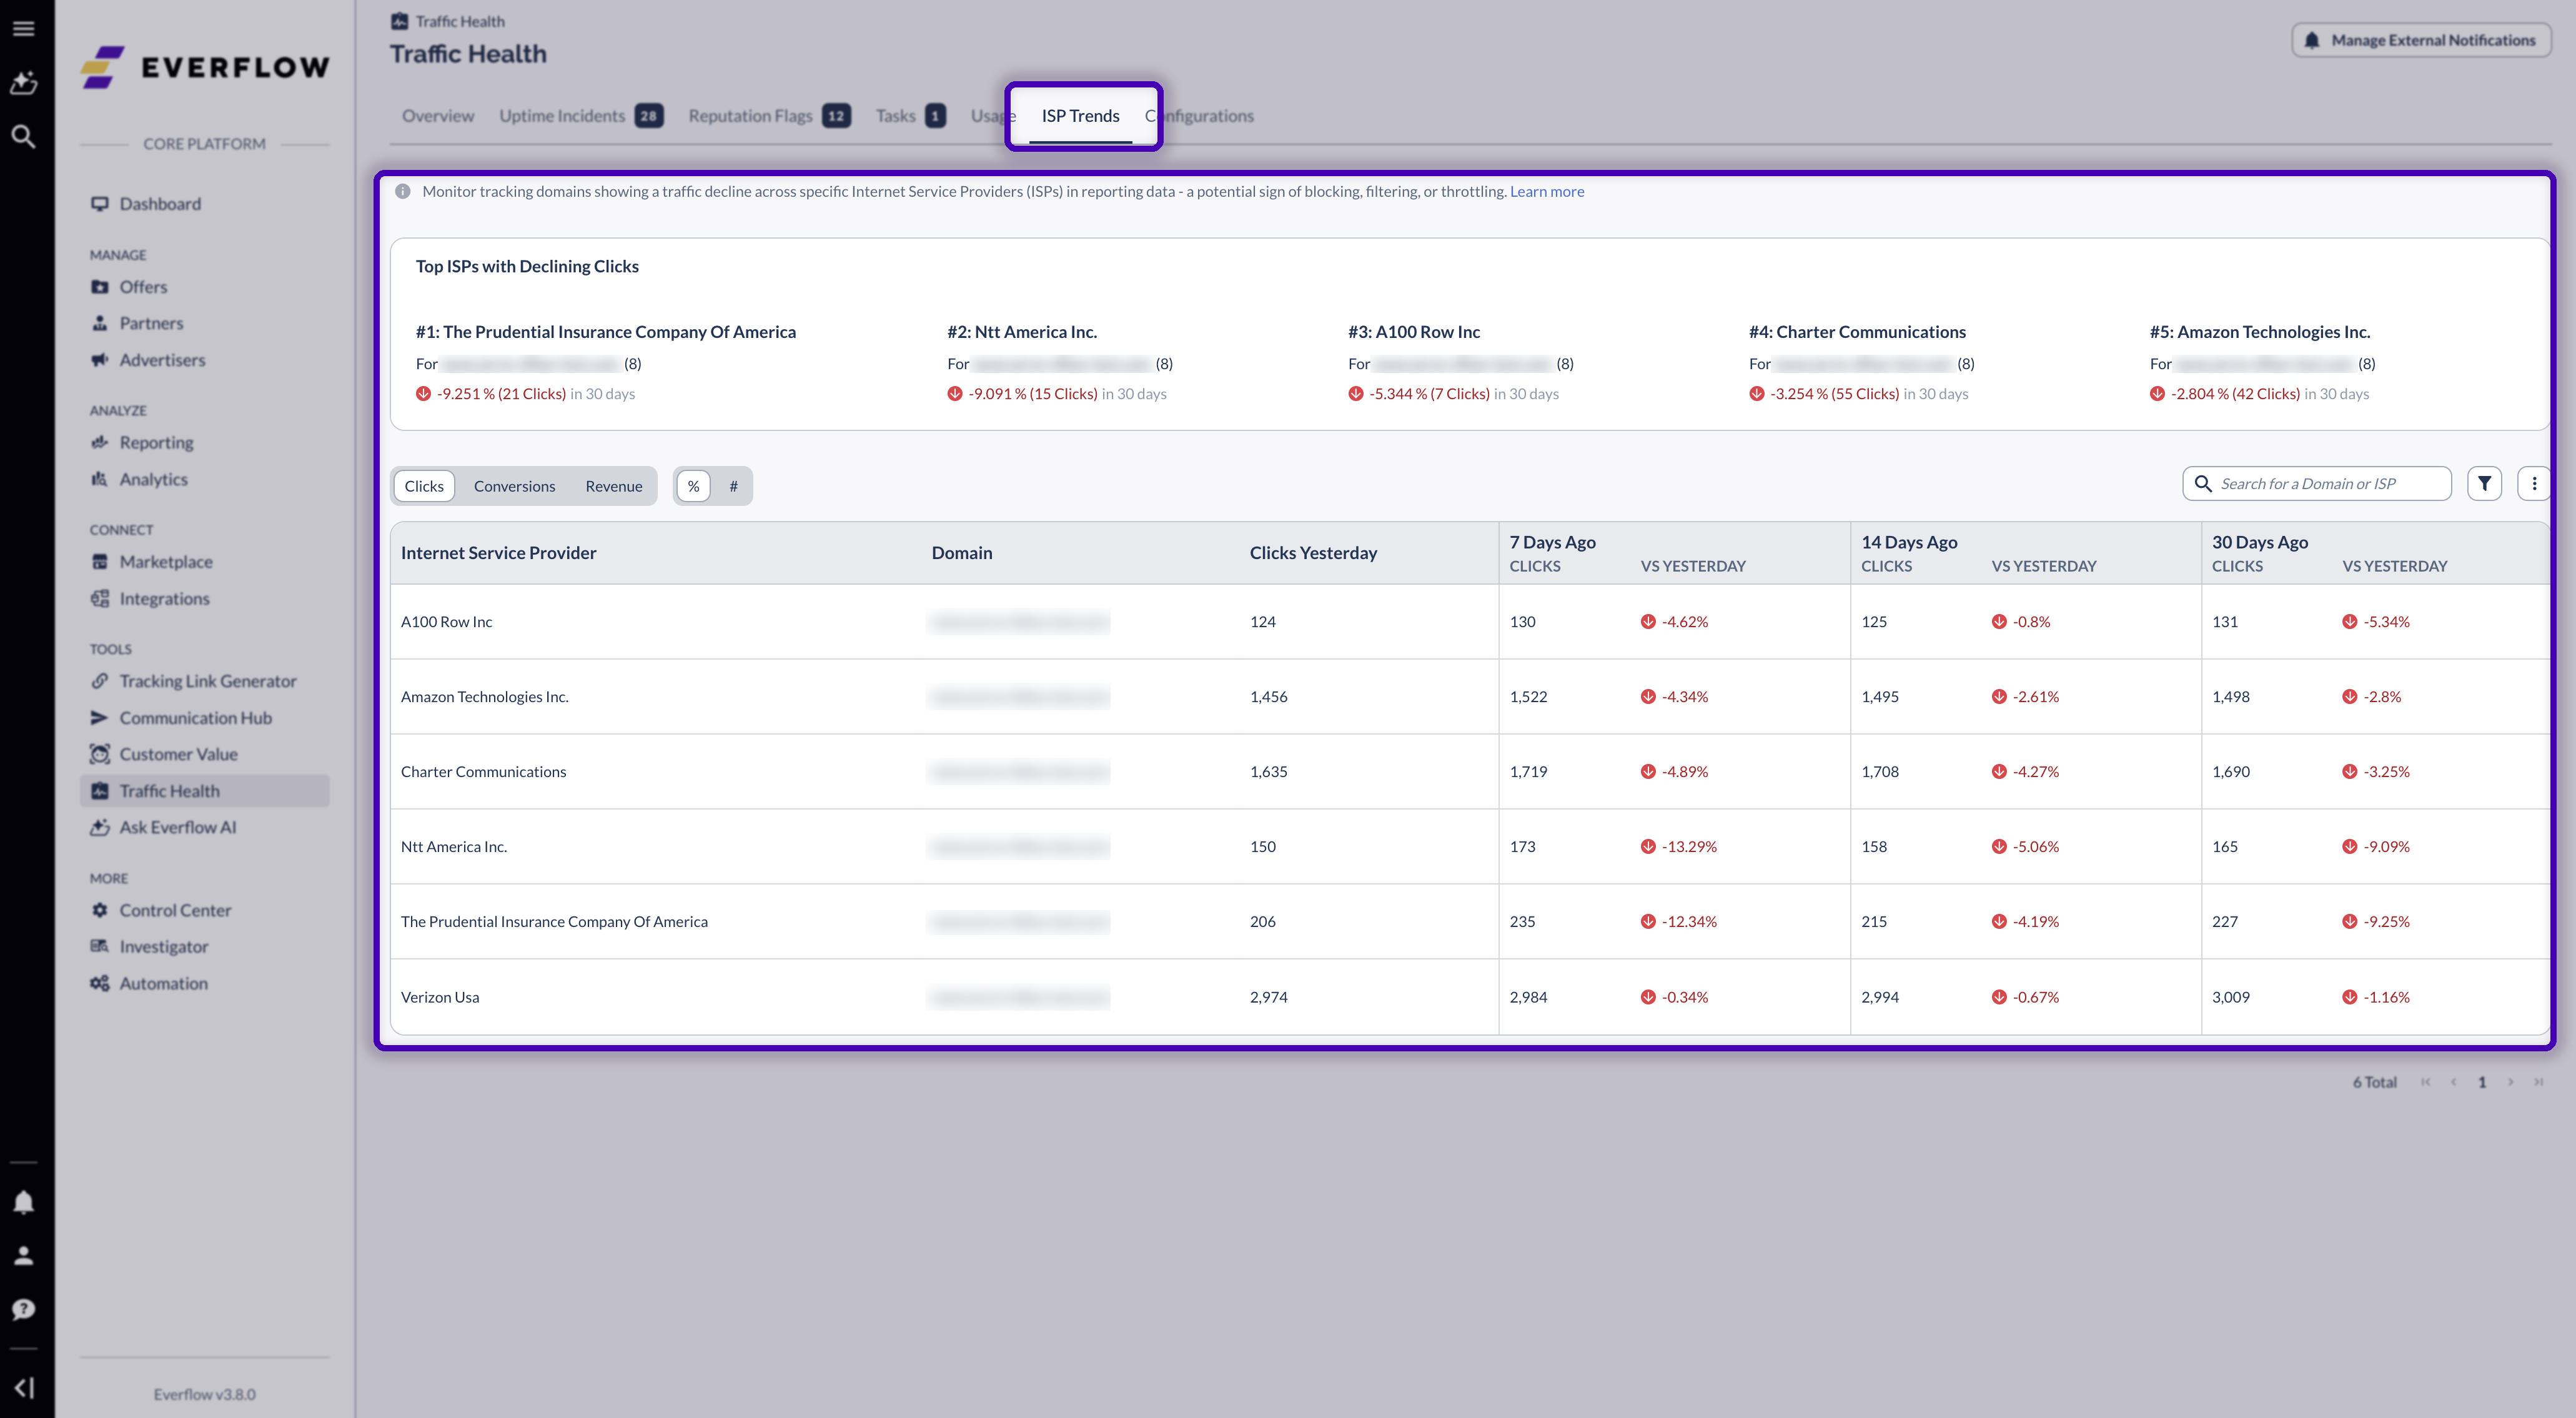
Top ISPs With Declining Clicks
The card at the top of the page is the short version of the whole report. It ranks the providers where your domains have lost the most traffic, so you can see at a glance whether anything needs attention without reading the table underneath.
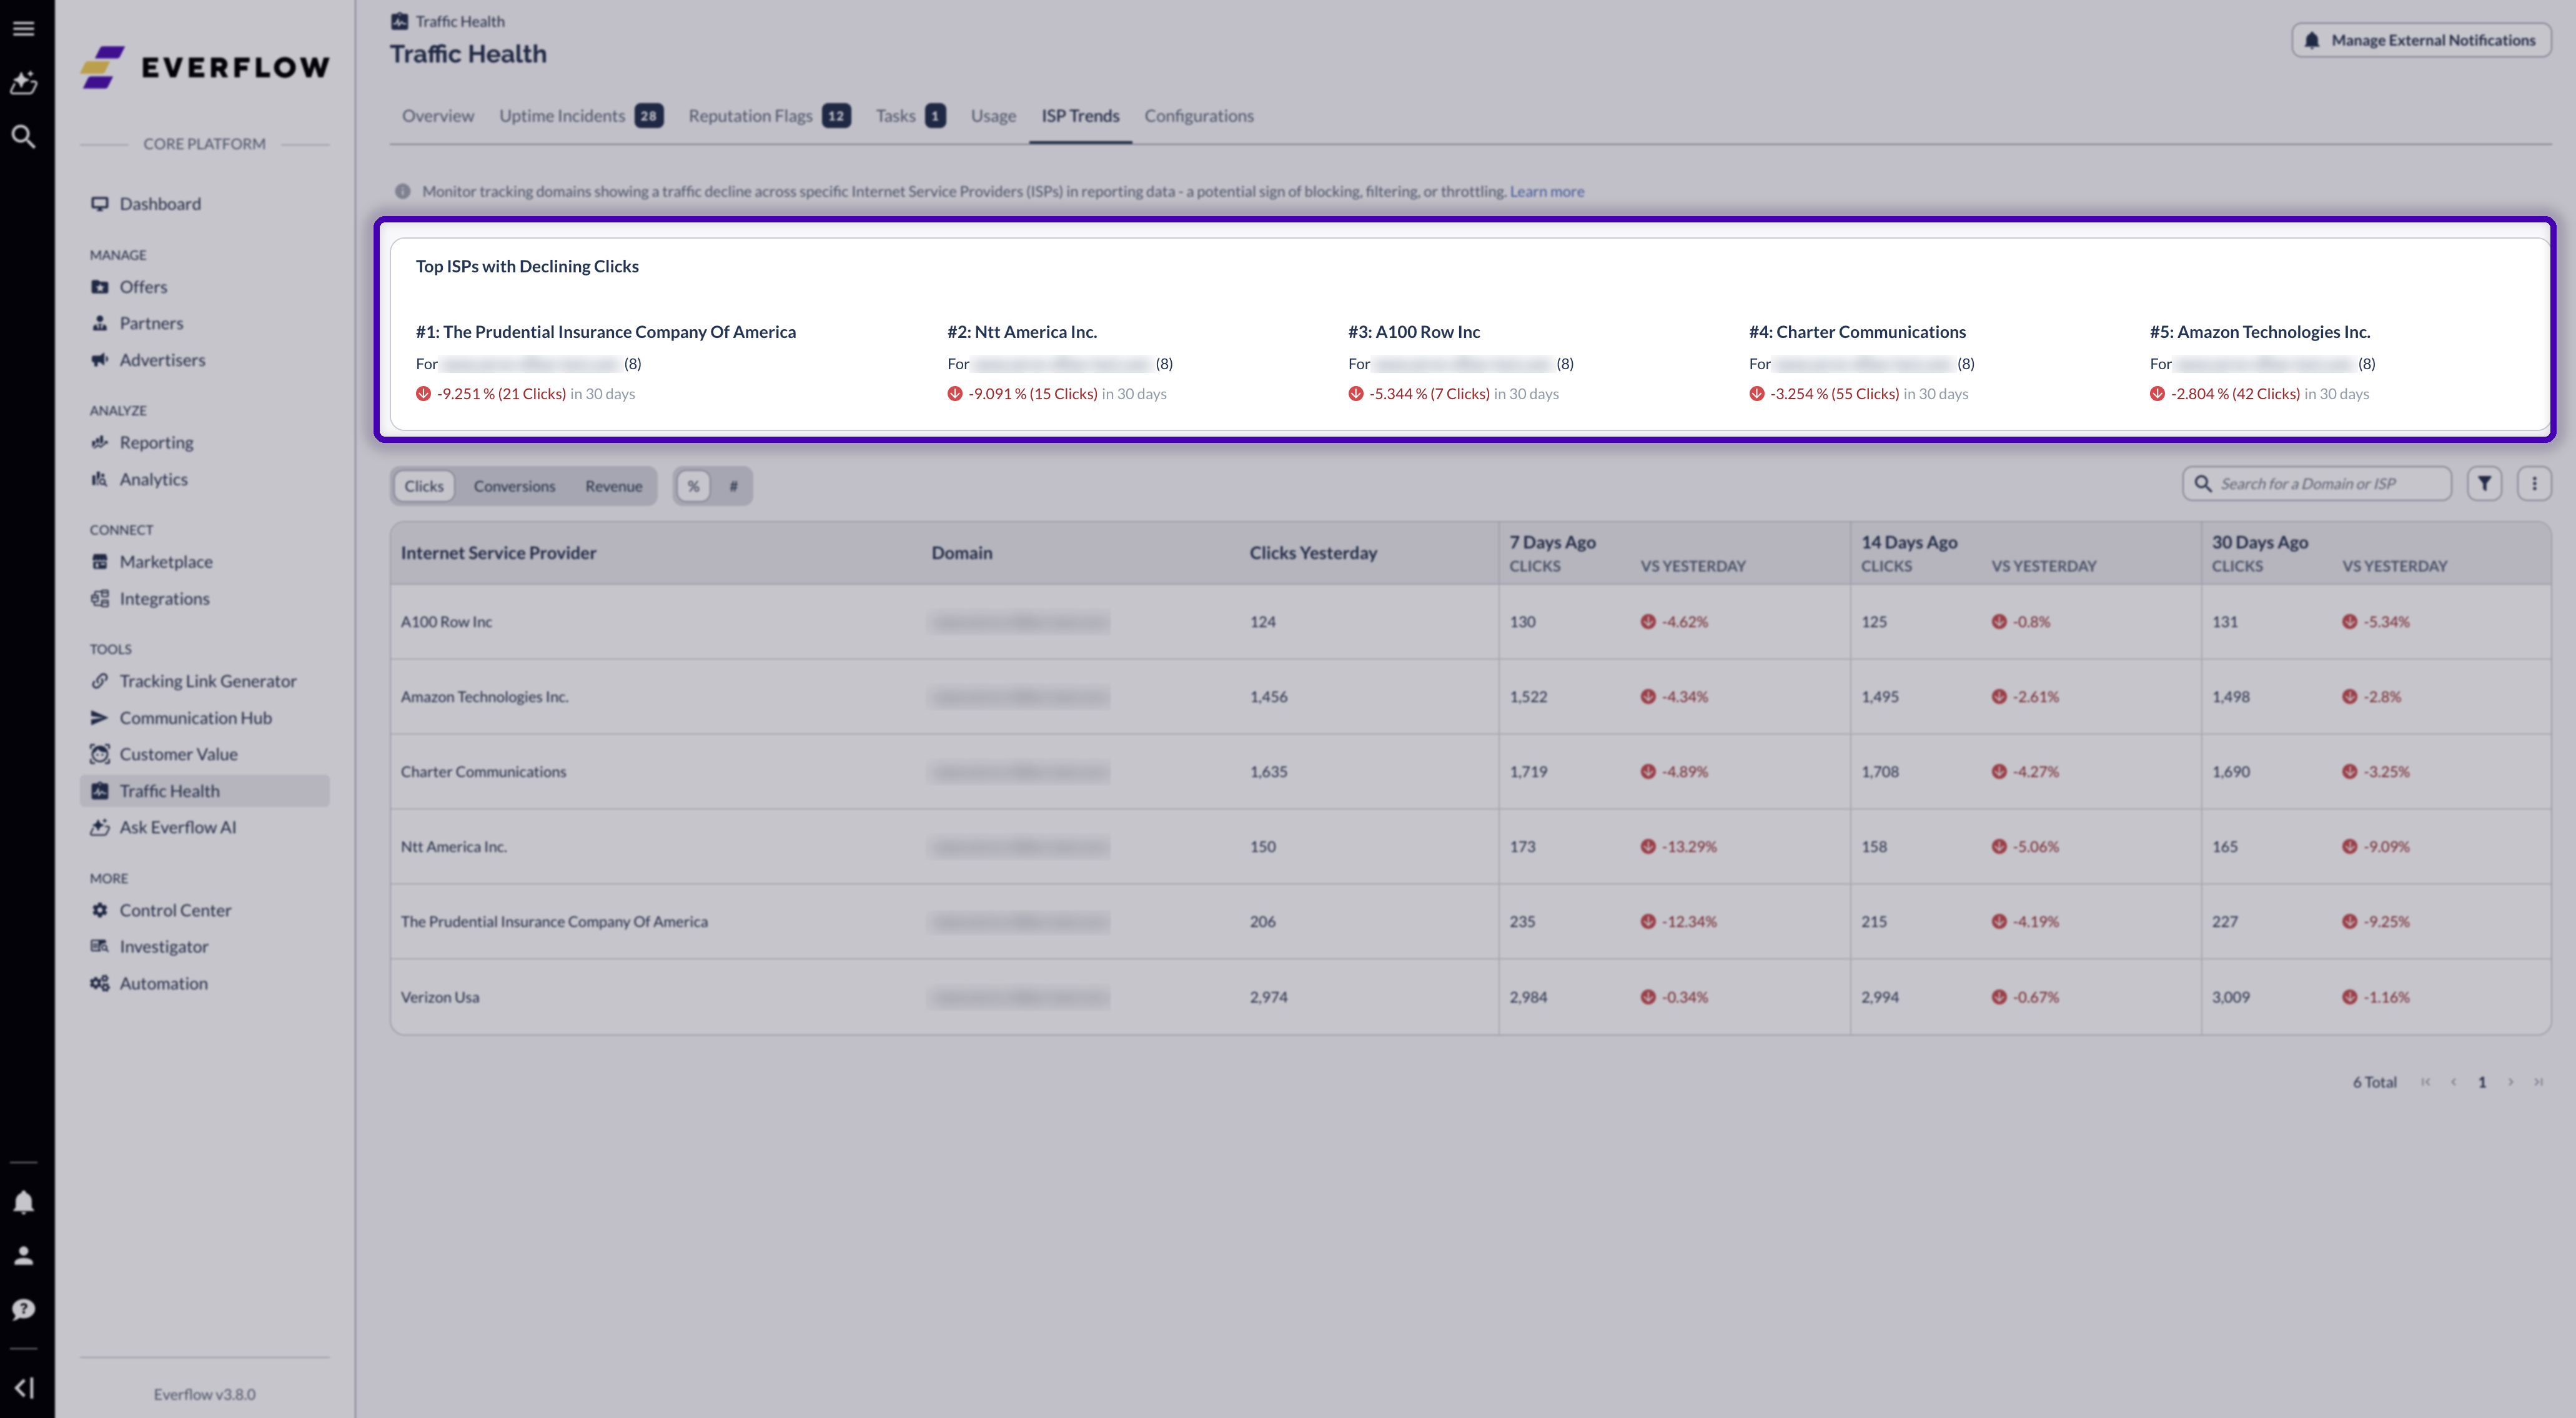
The card is limited to providers with meaningful volume behind them, so a domain that only ever saw a handful of clicks from a provider will not appear here. If nothing is trending downward, the card and the table are both empty. That is the healthy state, not a loading problem.
Reading The Table
Each row pairs one provider with one of your tracking domains, and shows how traffic on that pairing has moved. Three controls change what the table is telling you.
The three comparison periods
Every row is compared against three windows at once: seven, fourteen and thirty days ago, each with its own value and its own change against yesterday.
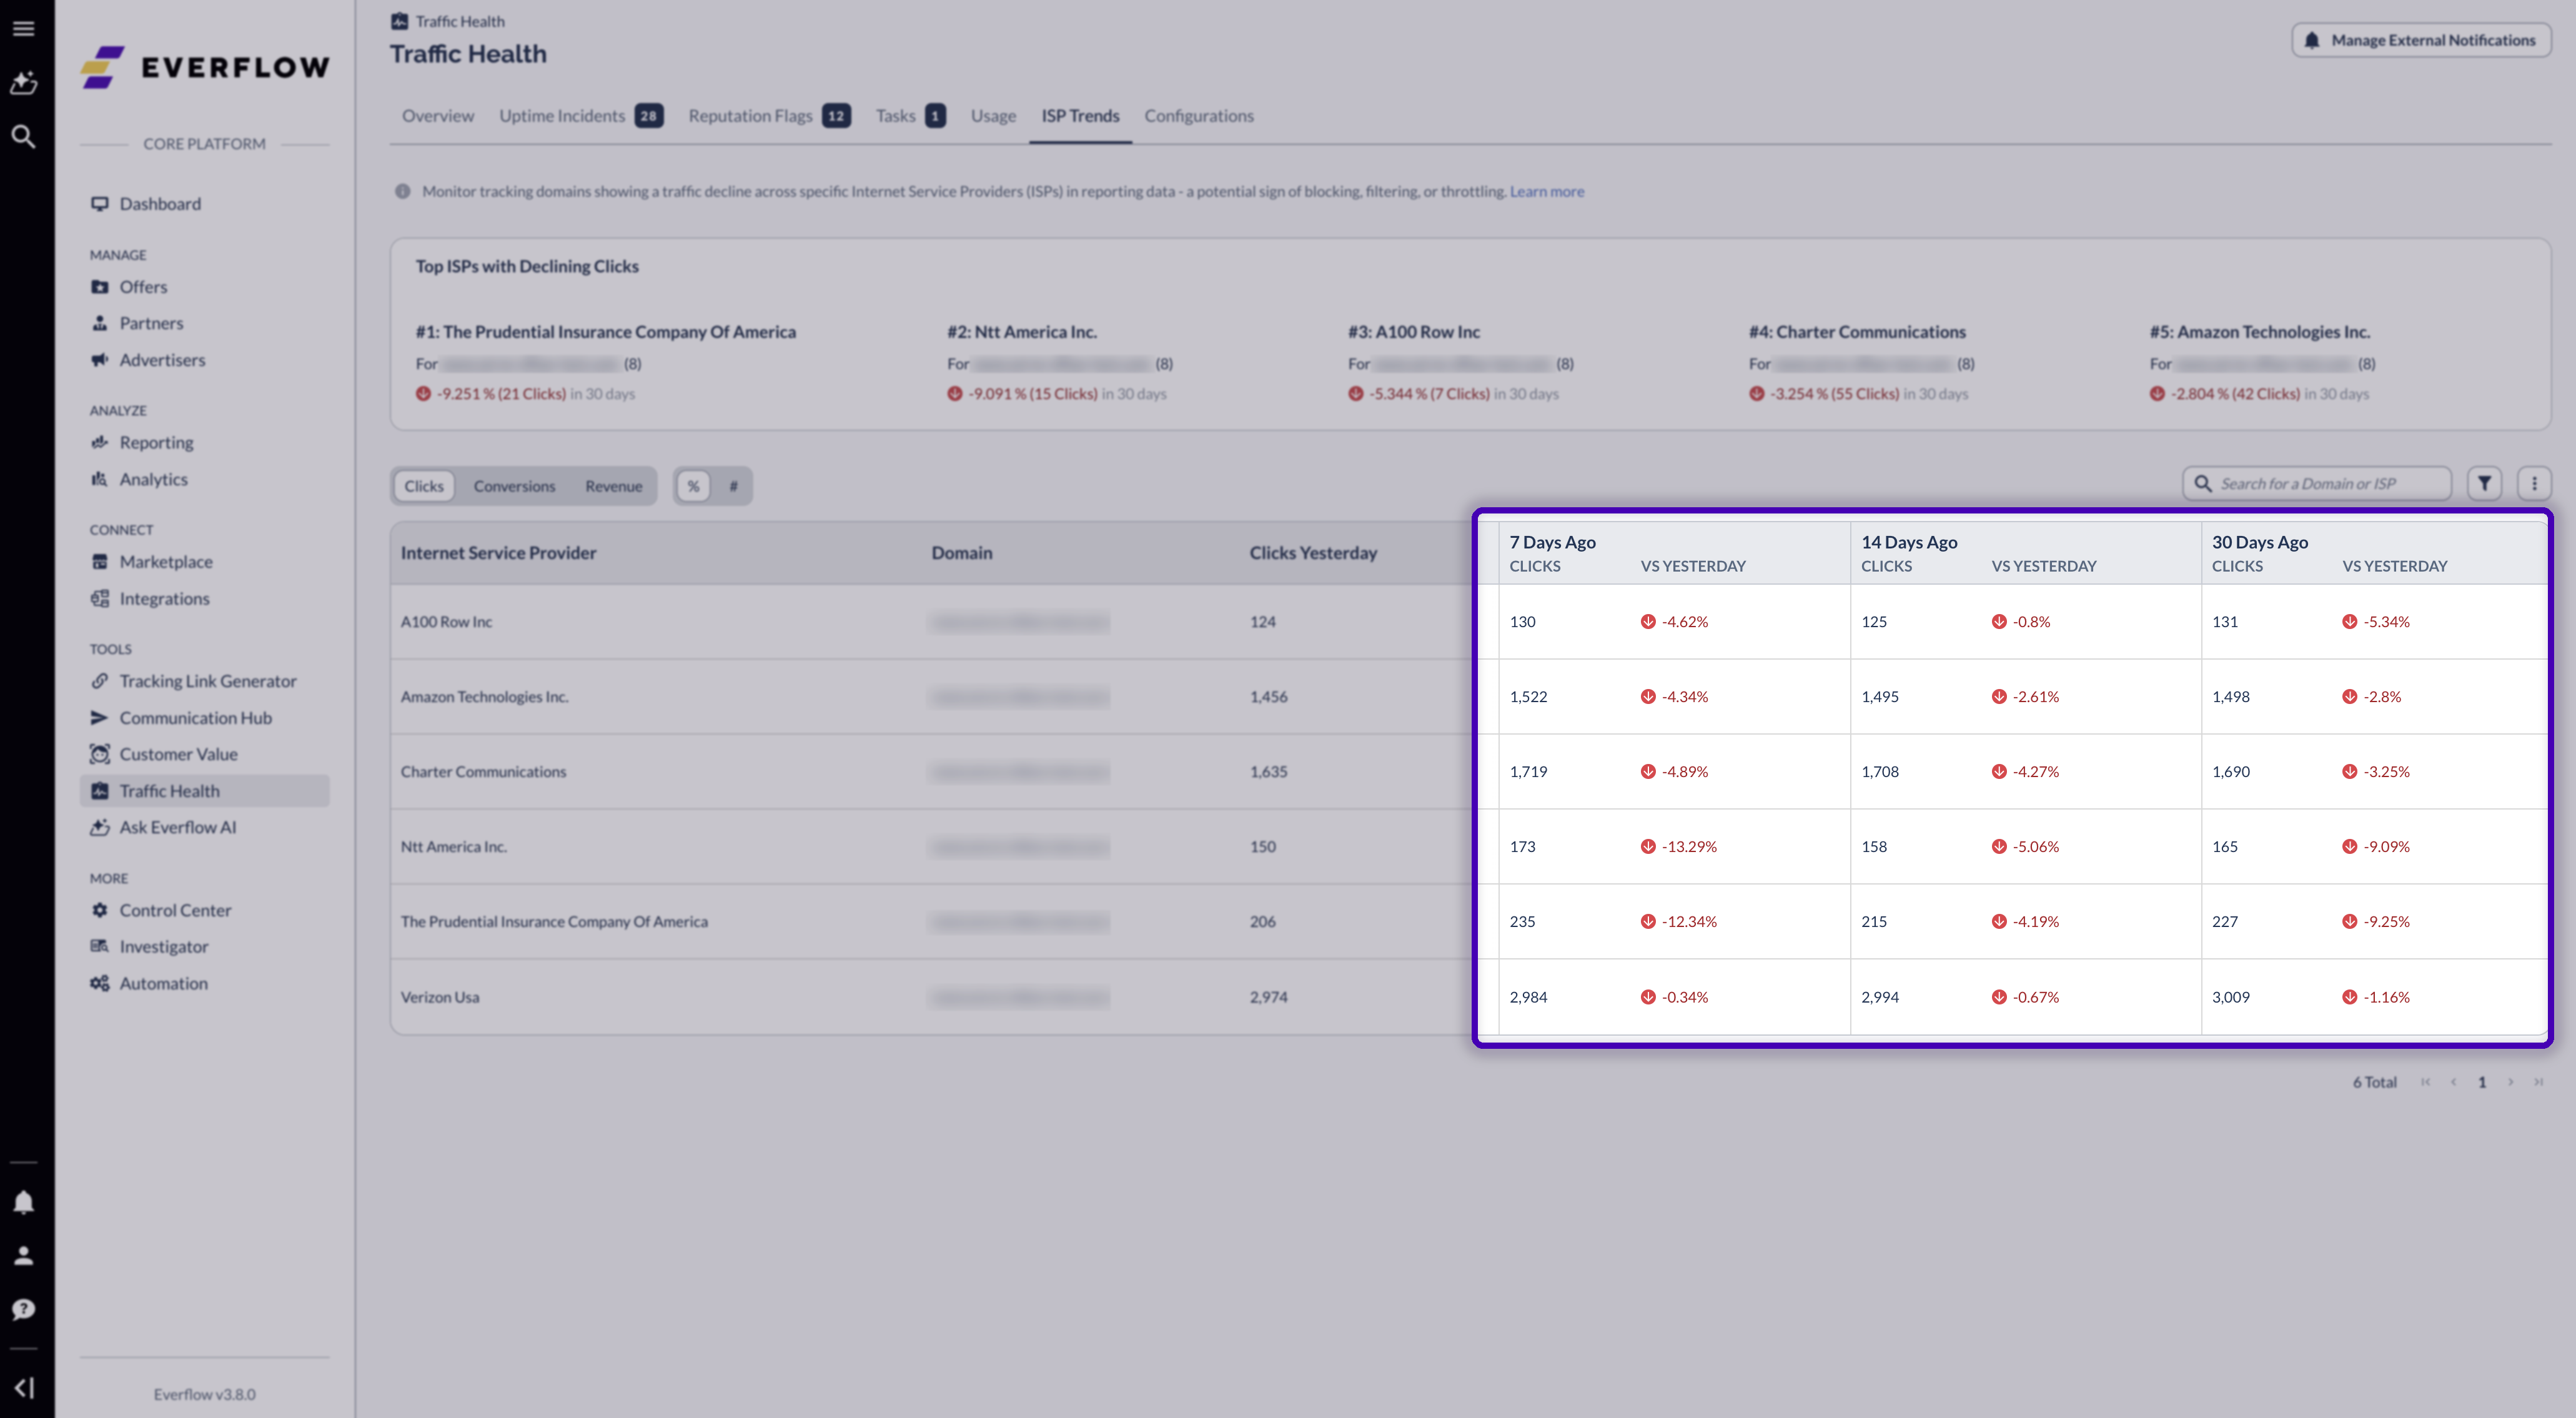
Reading all three together is what separates a real problem from noise. A drop that shows up against seven days but not against thirty is usually a partner pausing or a weekday pattern. A drop that deepens as the window widens is the shape worth investigating.
Choosing what to measure
The table can be built on clicks, conversions or revenue, and the change can be shown as a percentage or as a raw count.
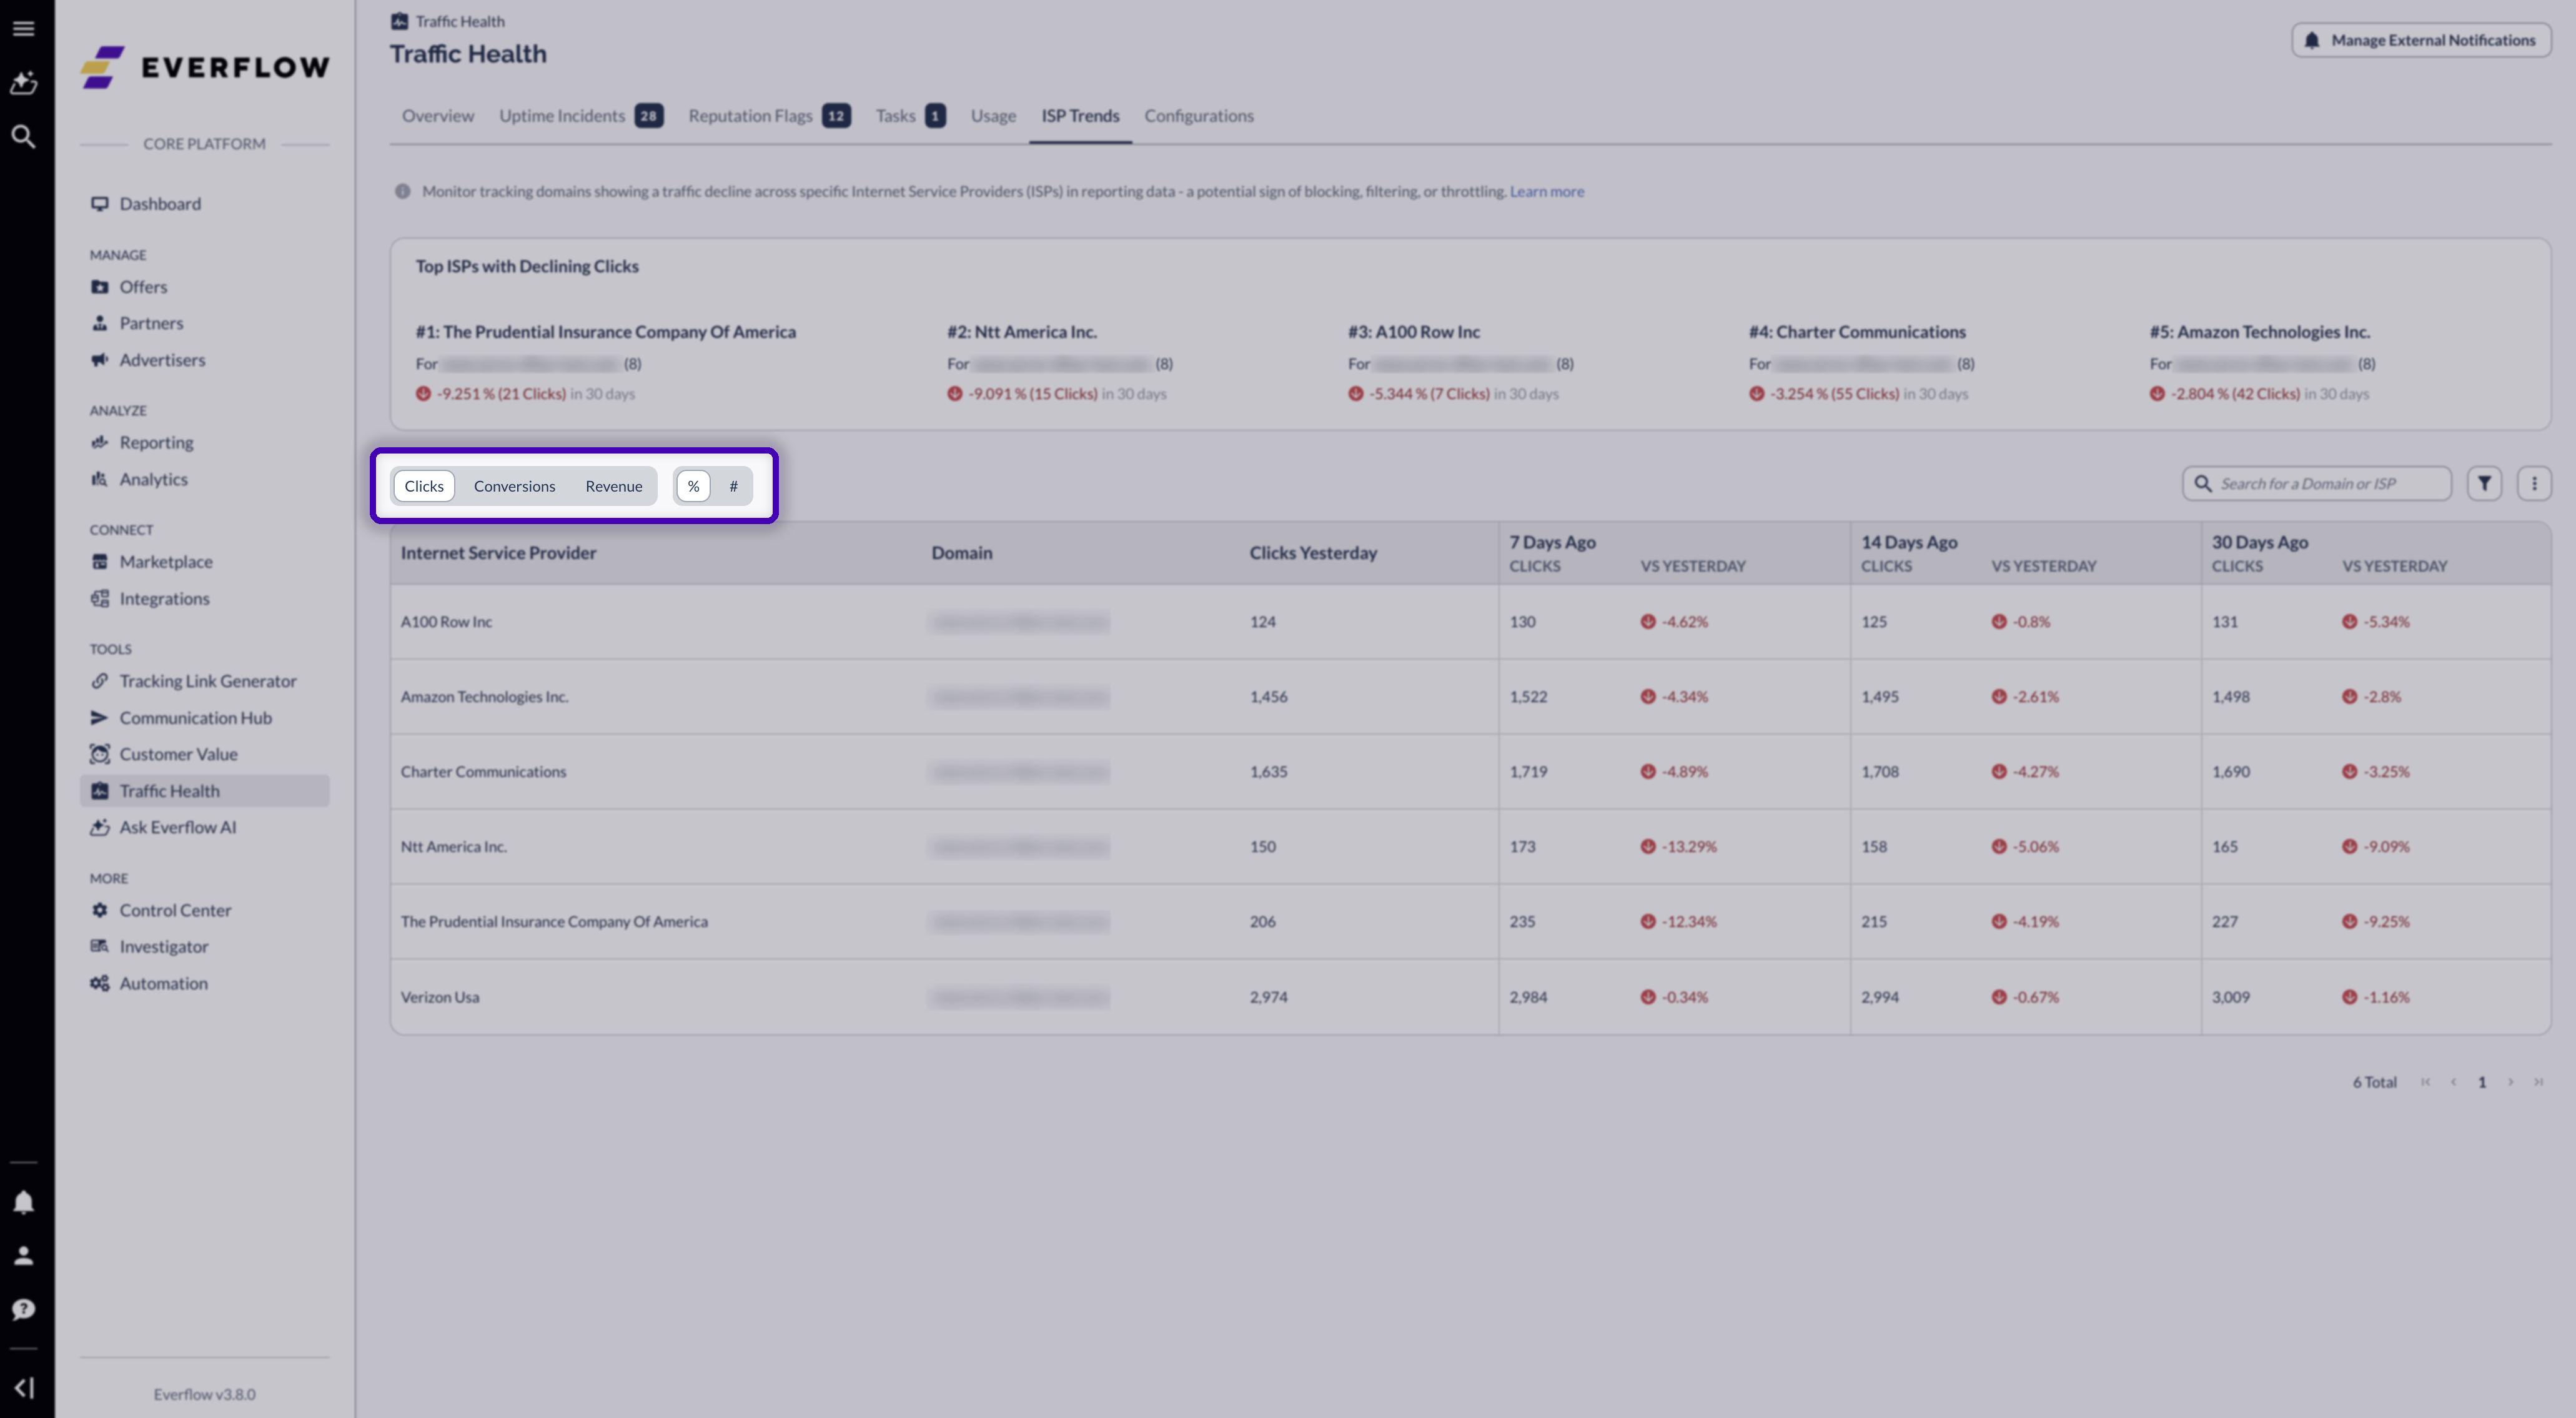
Clicks is the right default here. A domain that is unreachable loses clicks before it loses anything else, so clicks move first and move most clearly.
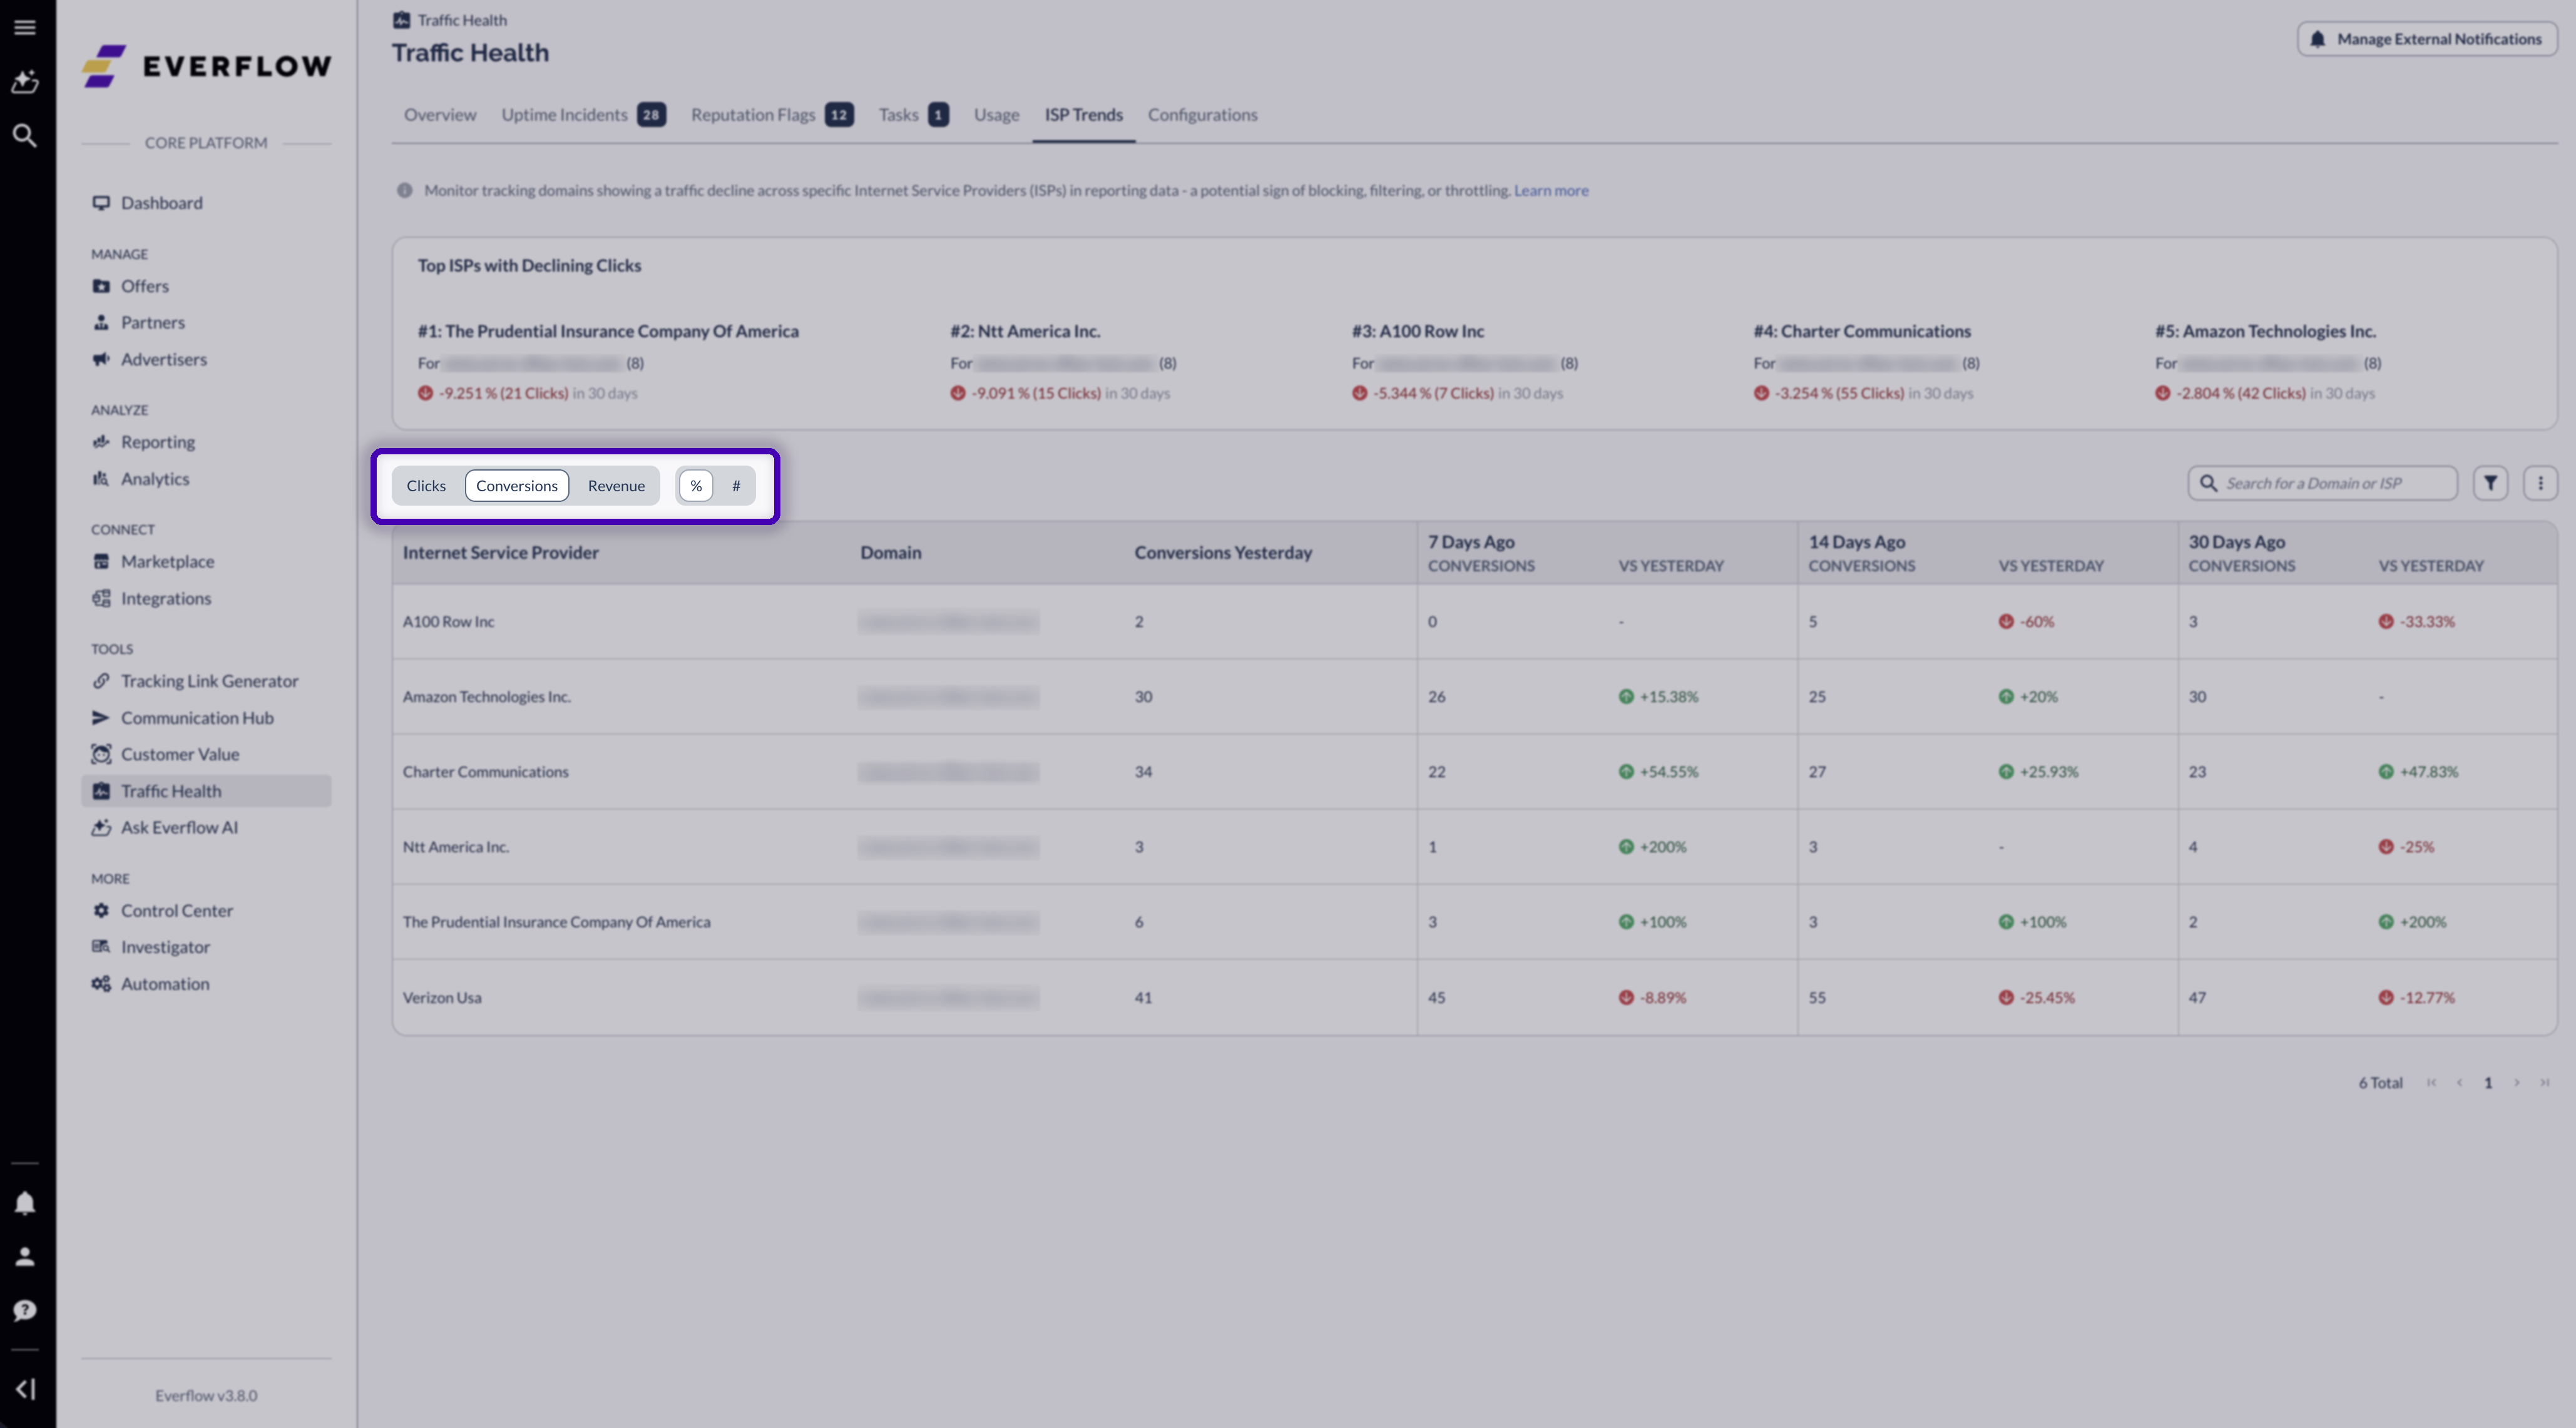
Conversions are worth a second pass, because they answer a different question. Clicks holding steady while conversions fall away on one provider points at something happening after the click, a script not loading for example, rather than the domain being unreachable.
Percentages or absolute numbers
The percentage view is the one to scan with, because it makes a collapse obvious regardless of how much volume the provider sends. The absolute view is the one to decide with.
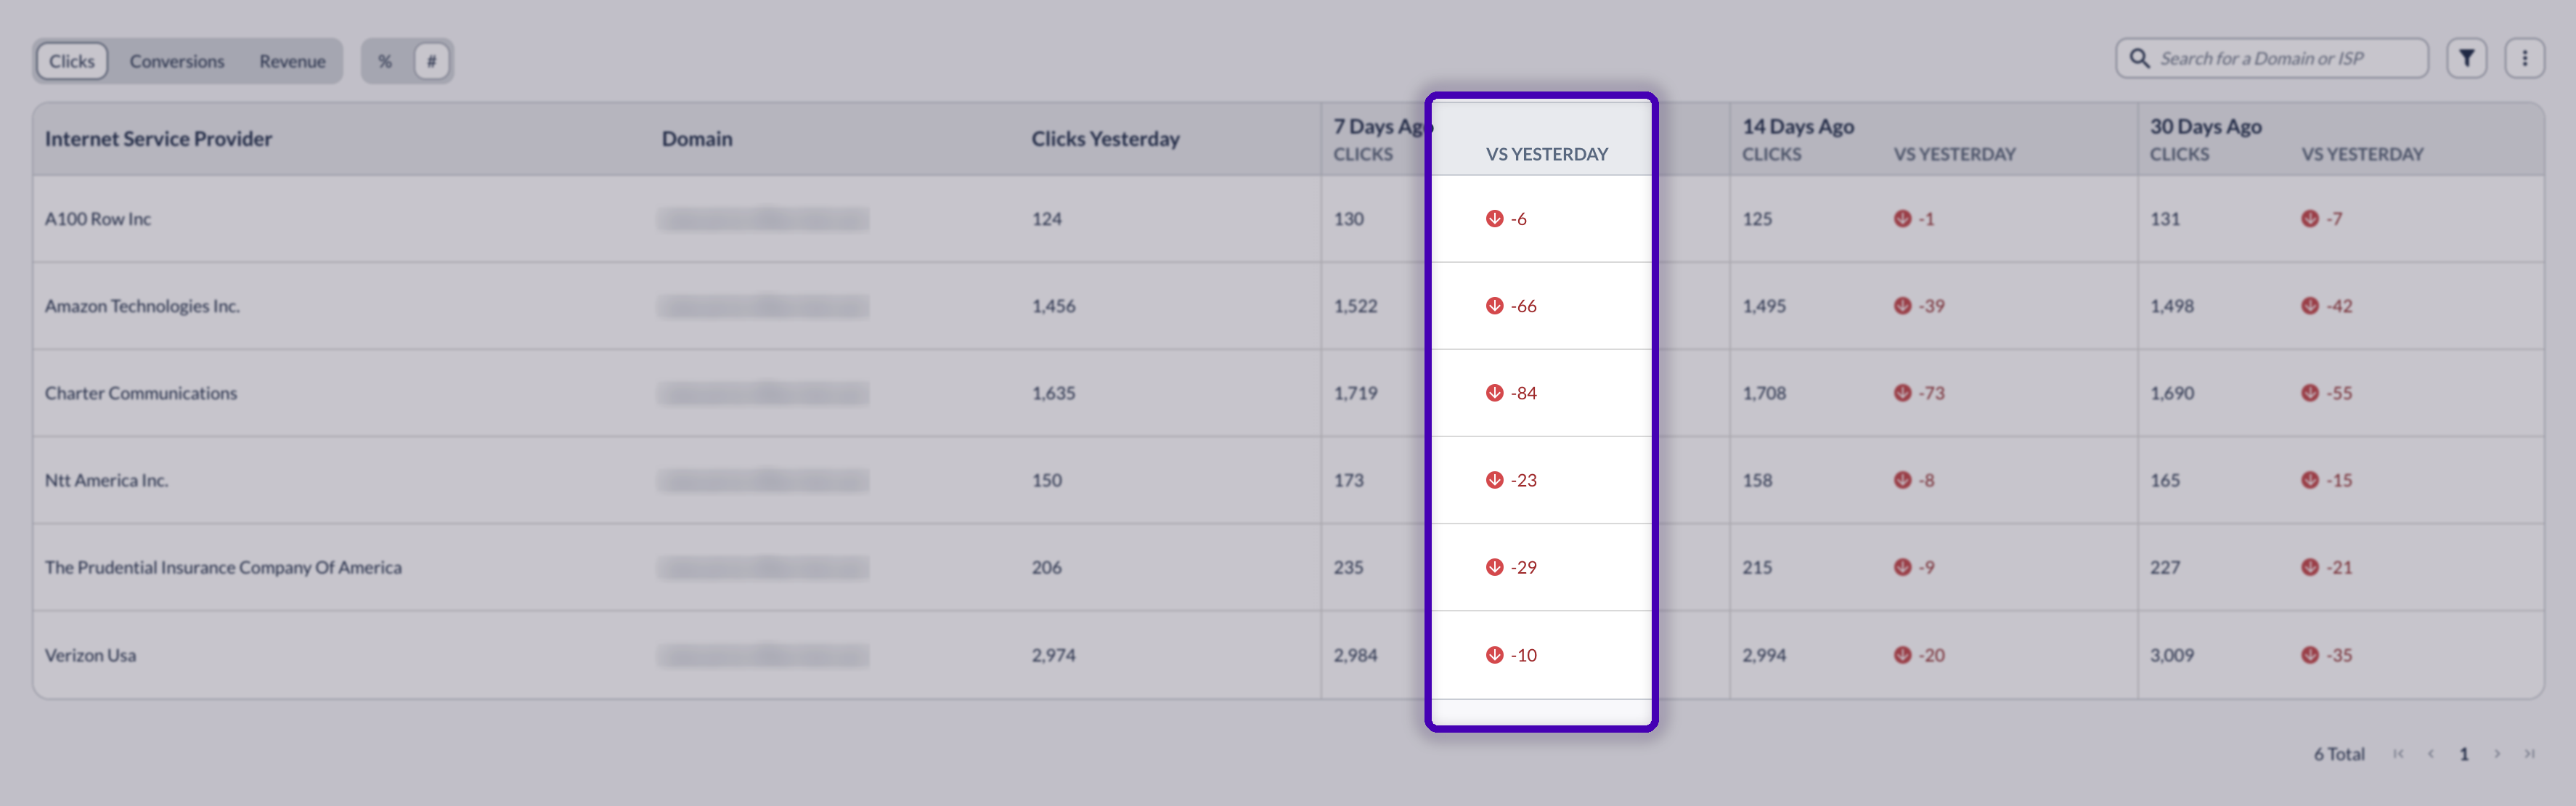
A ninety per cent drop on a provider that sends twenty clicks a day is not worth an afternoon. The same percentage on a provider carrying a fifth of your volume is. Switch to absolute numbers before deciding what to act on.
Narrowing The View
Filtering by domain or ISP
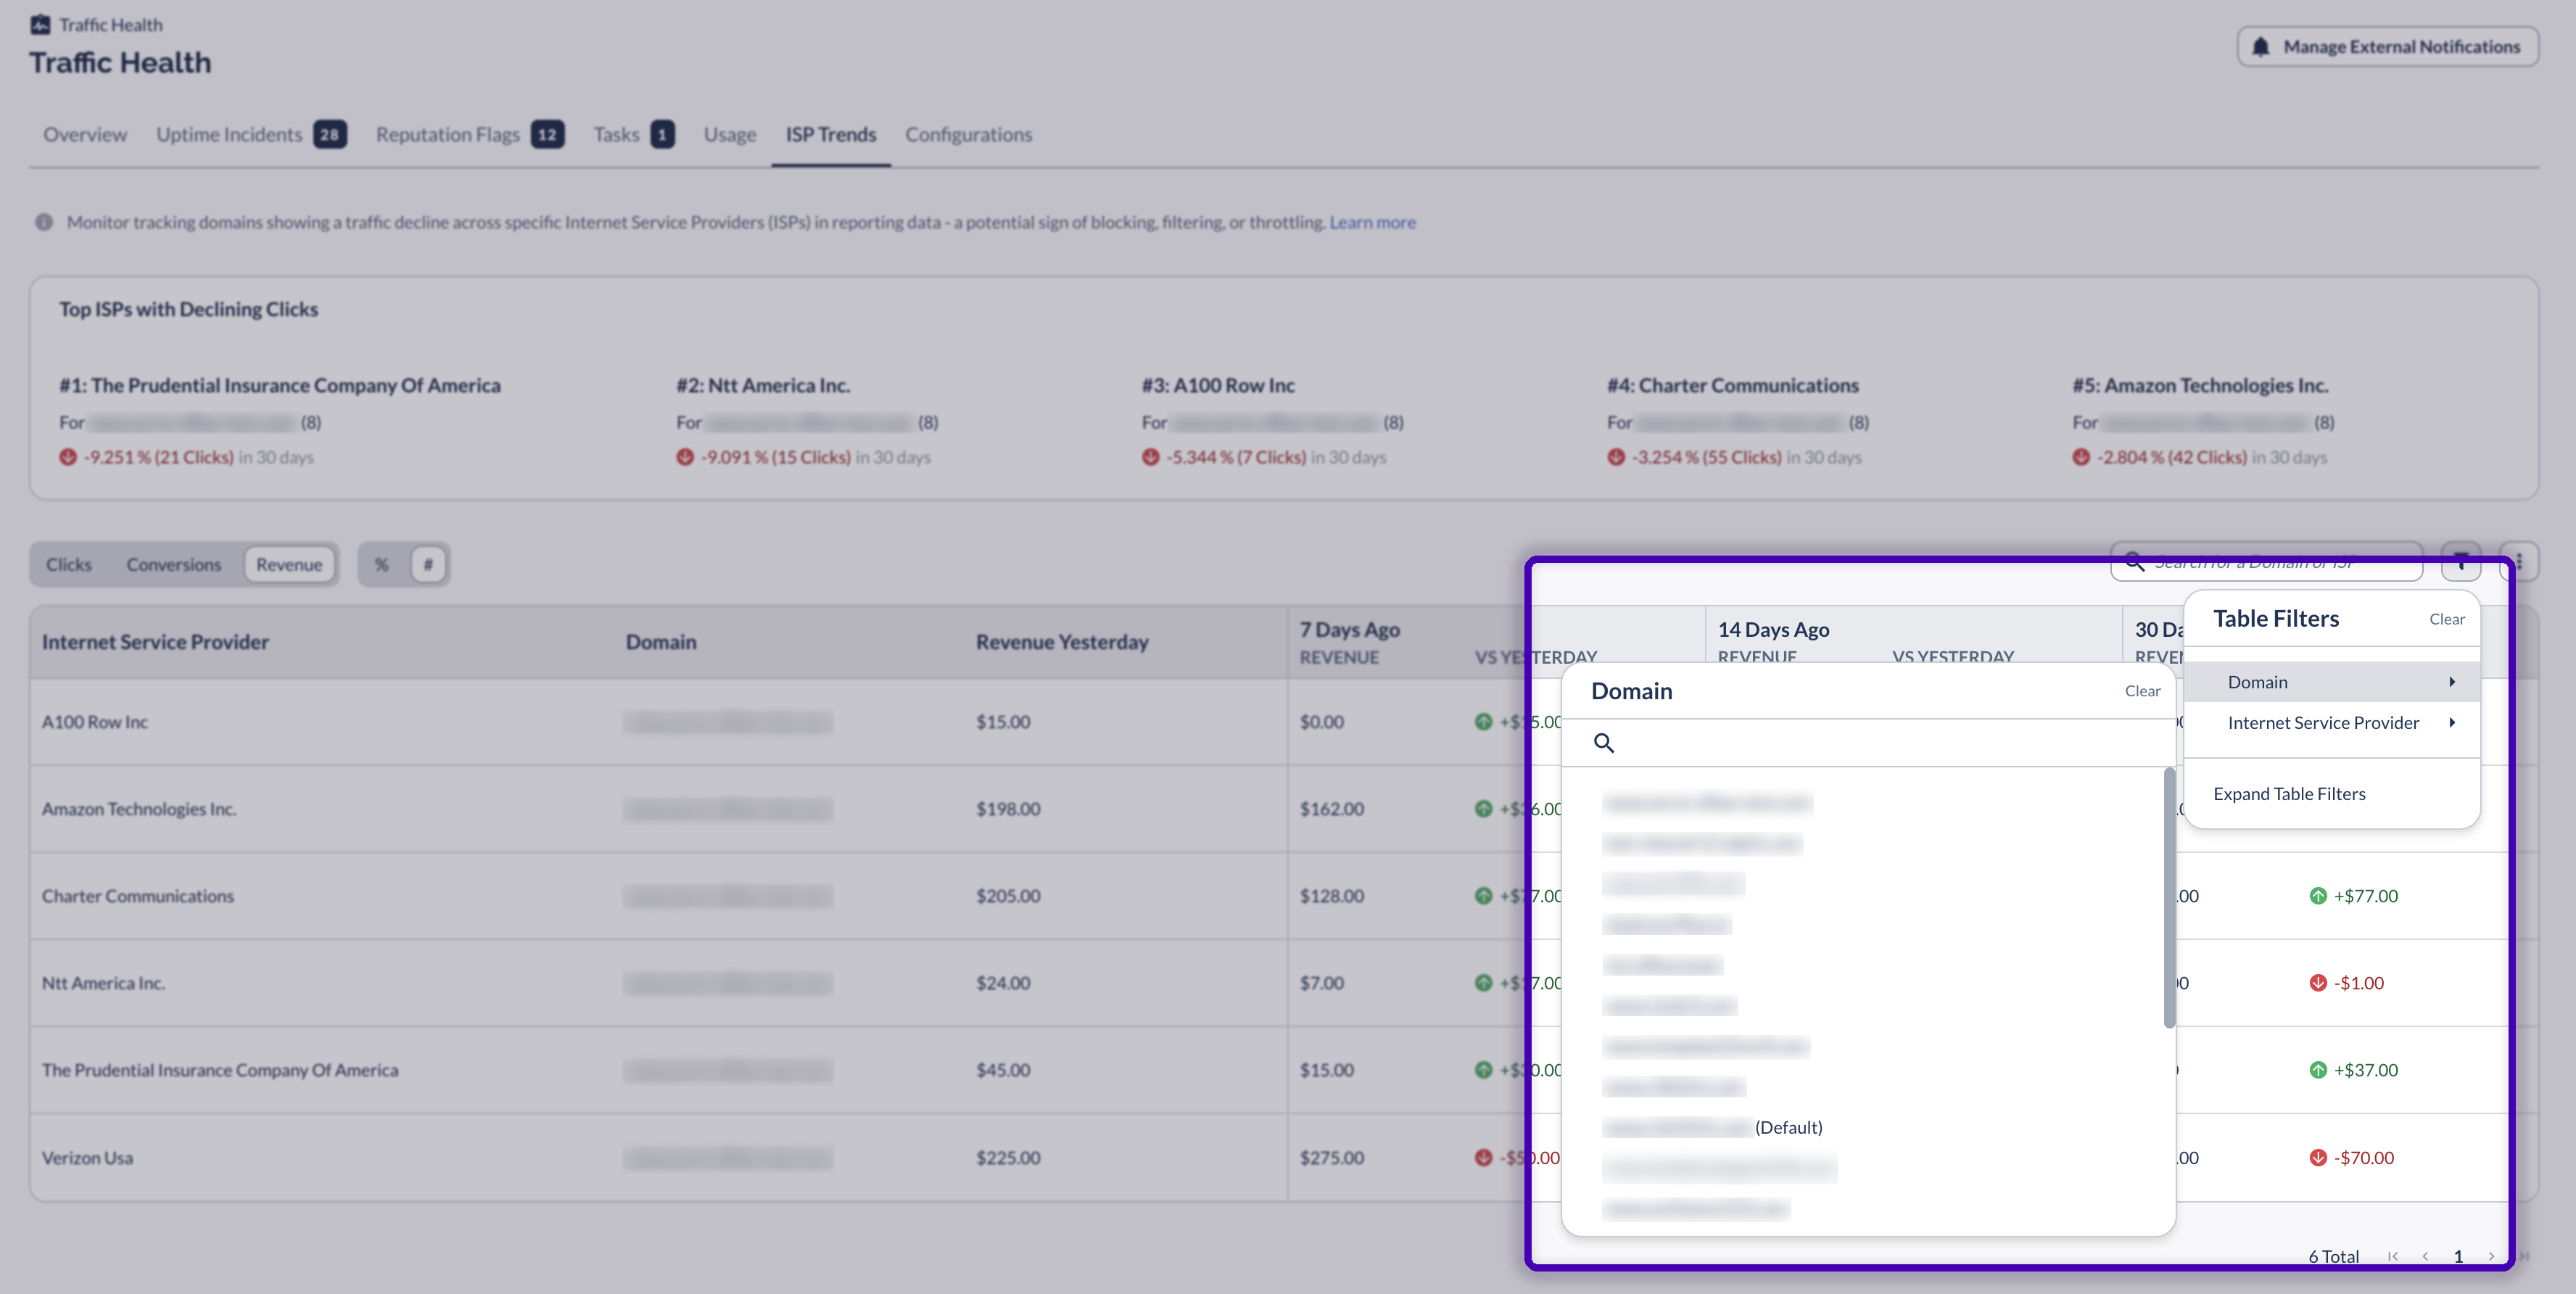
Filtering by domain answers the most useful diagnostic question in the whole report: is this happening to one domain, or to all of them? A decline isolated to a single domain points at that domain. The same decline across every domain you run usually points at something else entirely: a change on your pages, or a shared piece of infrastructure sitting in front of them.
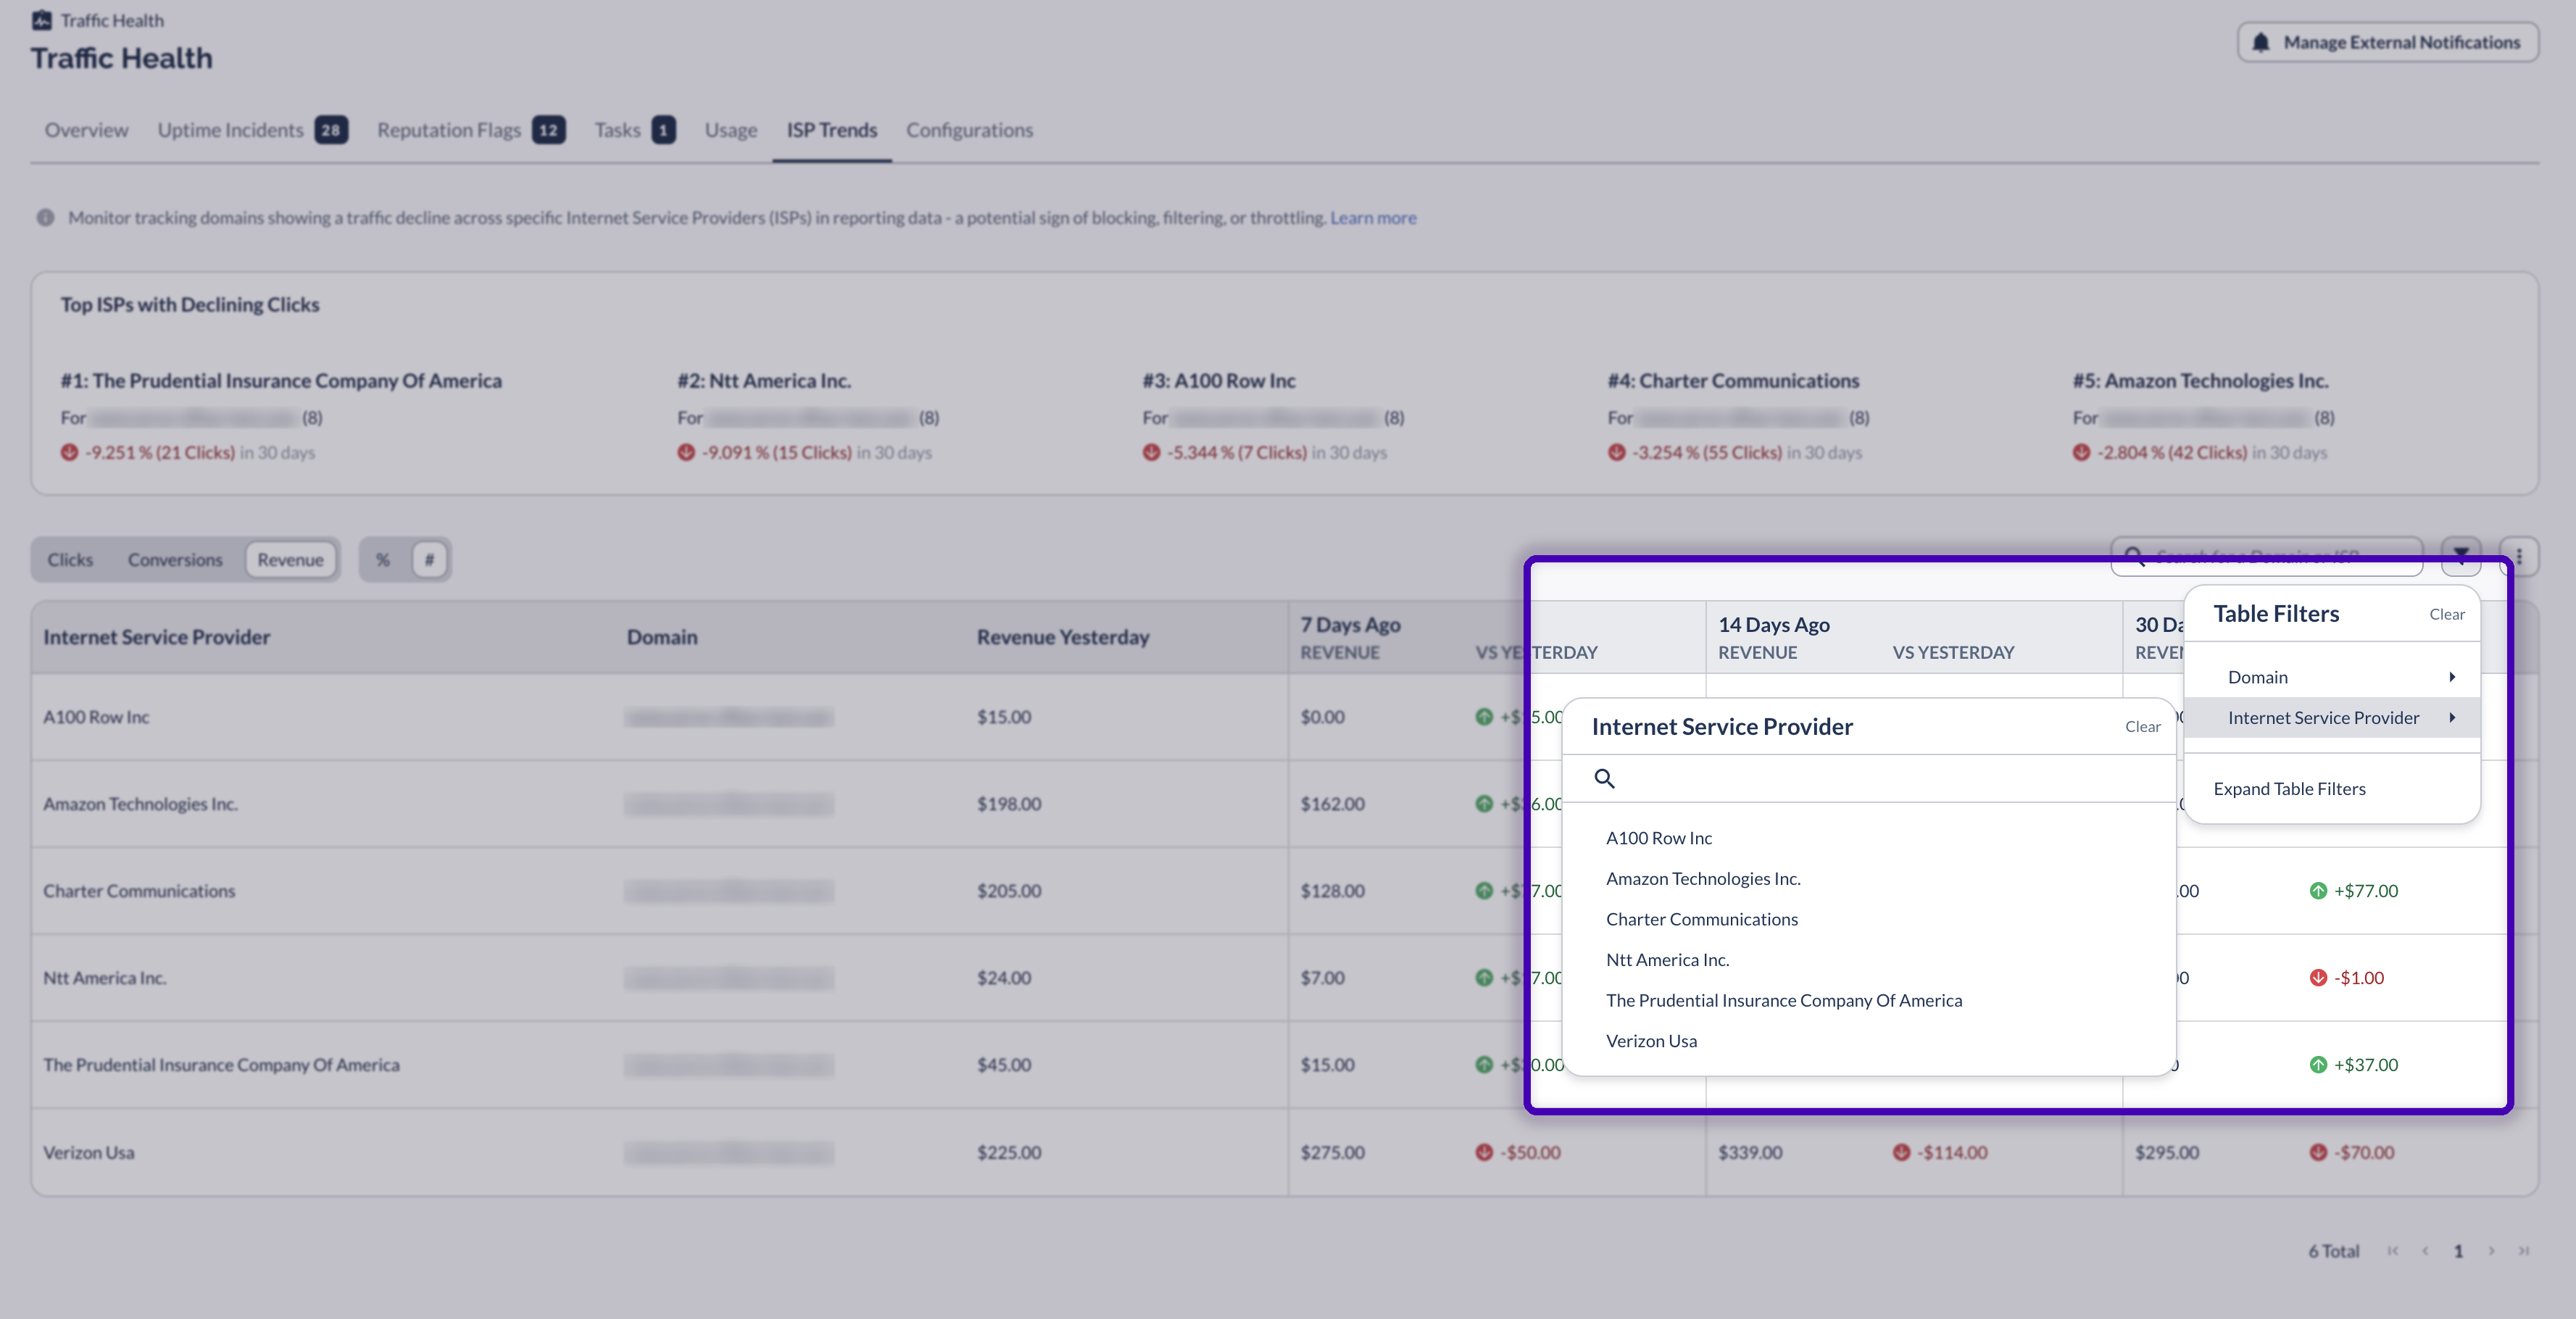
Filtering by provider is how you follow up a partner report. If a partner tells you their traffic died and names their carrier, filter to that carrier and see whether your own data agrees.
Choosing which columns to show
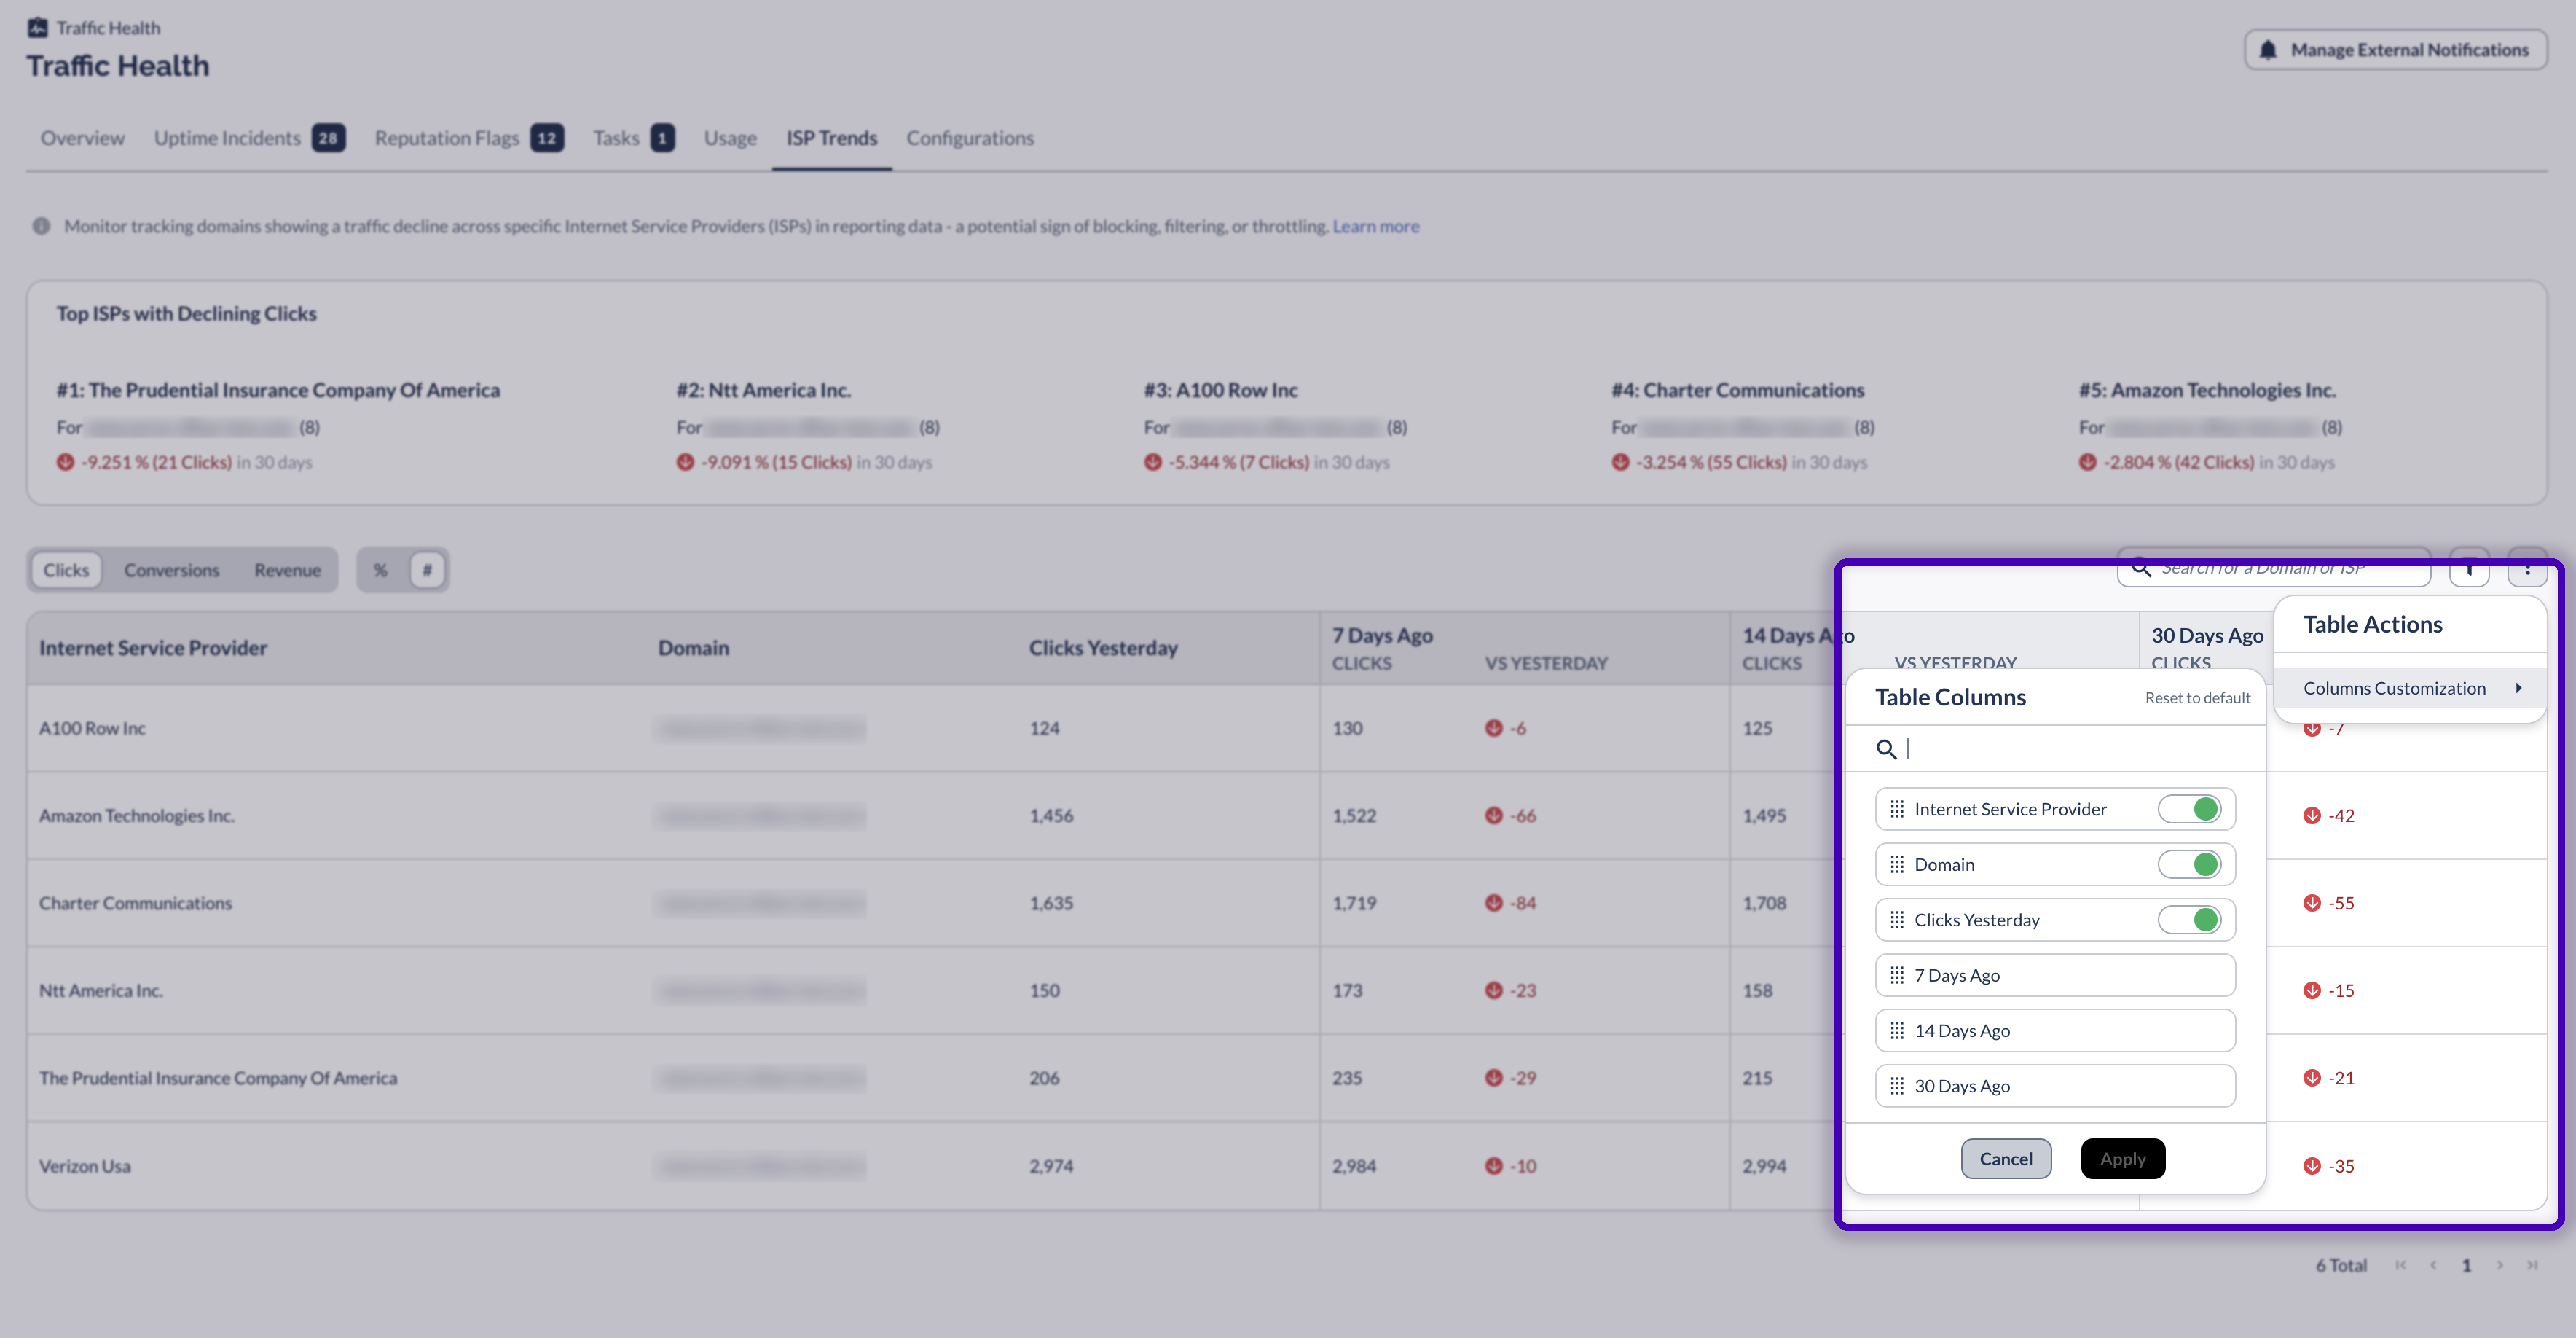
Turning off the comparison periods you are not using makes the table considerably easier to scan, particularly if you are checking it regularly.
How Big A Drop Matters
There is no threshold at which a decline becomes a confirmed block. These are the working ranges our team uses when reading the report.
The most informative check is not the size of the drop but its spread. If every partner sending traffic through a domain has lost that provider, the domain is the common factor. If one partner has lost it and the others have not, look at what changed for that partner. A campaign ending is far more likely than a block.
When A Provider Is Blocking Your Tracking Domain
Consumer internet providers and mobile carriers increasingly ship network-level security products, sold under names like Xfinity Advanced Security, Verizon Home Network Protection, AT&T ActiveArmor and Videotron Helix Safety. These block domains their providers associate with tracking or with poor reputation, and they do it for the whole household or the whole mobile connection rather than in one browser.
Networks in Canada see this with Videotron, Rogers and Bell; in the United States it comes up most often with Verizon, T-Mobile, Comcast and Xfinity, AT&T and Spectrum.
This is a real cause and it is worth knowing about. But it is not the only thing that produces these symptoms, and reaching for it first has sent people down the wrong path more than once. Work from the symptom instead. Select the one you are seeing:
Working Through It
In order, cheapest first. Each of these has resolved a real case.
What Traffic Health Can And Cannot See
Traffic Health watches your domains and their IPs against reputation and blocklist sources (Google Threat Intelligence, HetrixTools and EasyList among them), and where one of them flags a domain, it names the source so you know where to appeal. In practice this catches more of these cases than people expect.
What it does not have is visibility into the private lists that consumer network-security products maintain. Those are not published and cannot be queried, so a domain can be blocked by one of them while Traffic Health shows nothing.
Common Questions
Because reachability depends on the network the request comes from, and often on the region. A domain can be perfectly reachable on your connection and unreachable on a particular mobile carrier in a particular area. Testing from your own connection tells you almost nothing. You need someone on the same provider to test it.
No, but it is still the right first check, and it is right more often than people expect. Traffic Health monitors a wide set of reputation and blocklist vendors, and several cases that were first assumed to be provider-level blocking turned out to be ordinary flags that Traffic Health does report. What it does not have is visibility into the private lists that consumer network-security products maintain, so a clean Traffic Health result narrows the problem rather than closing it.
No. The certificate on your tracking domain is valid, and the same link loads normally from another network. The error means the secure connection was interrupted before it finished being set up. Reinstalling or reissuing a certificate will not change it.
That happens, and when it does, domain reputation is not the explanation. A domain that has never carried traffic has no reputation to be flagged on. Work through the checks in Working through it above. In practice the causes that survive a domain change have been a blocked script path, security settings on a proxy in front of the tracking domain, or a resolution failure on the end user’s network.
No. A domain hosted by Everflow carries no inherent reputation advantage over one you bring yourself. What matters is the domain’s own history and the behaviour of the traffic running through it.
No. Consumer network-security products and reputation vendors are outside the platform, and they only accept appeals from the party responsible for the domain. Where a vendor is named in Traffic Health, the delisting route is that vendor’s own false-positive process. Networks that do this regularly report appeals usually coming back the same day.
Not automatically. Rotation used to be the standard answer and it is now producing worse results for high-volume networks. Frequent rotation across similar-looking domains is itself a pattern that reputation systems key on. Networks that used to rotate are increasingly appealing the flag first and only moving the domain when the appeal fails.
Yes. Assigning a specific tracking domain to an individual partner is supported, and it is a common arrangement for partners whose traffic carries more risk. It also contains the damage: a flag picked up on that partner’s domain does not affect everyone else.
Yes. Changing the domain on your offers does not change links your partners are already using, so they need to take fresh links. You can update offers in bulk, and you can keep the previous domain live alongside the new one while partners migrate.
Your first domain is included with your Everflow account. Additional domains are $40 per month per domain, whether they are fully managed or co-managed, and this is billed separately from Traffic Health, so you do not need Premium to add domains. If you expect to need spares, it is worth having them in place before you need them rather than arranging one mid-incident. See Domain Management Options for what each management type covers.
Traffic Health does not roll them up. It monitors each hostname exactly as configured, so a root domain is only monitored if it is added separately as a third-party domain, which requires Traffic Health Premium. Whether an individual reputation vendor rolls a subdomain up to its root varies by vendor, and is not something we can answer for all of them.


